
Apps
SIM card vulnerability puts your sensitive information at risk
It’s called the SIMjacker

SIM cards are very important. However, a new SIM card vulnerability found out by AdaptiveMobile Security might be putting our information at risk. The Simjacker exploit, which was recently found out and still being investigated on, allows malicious hackers to steal sensitive information from your phone through a SIM card.
Mechanism of attack
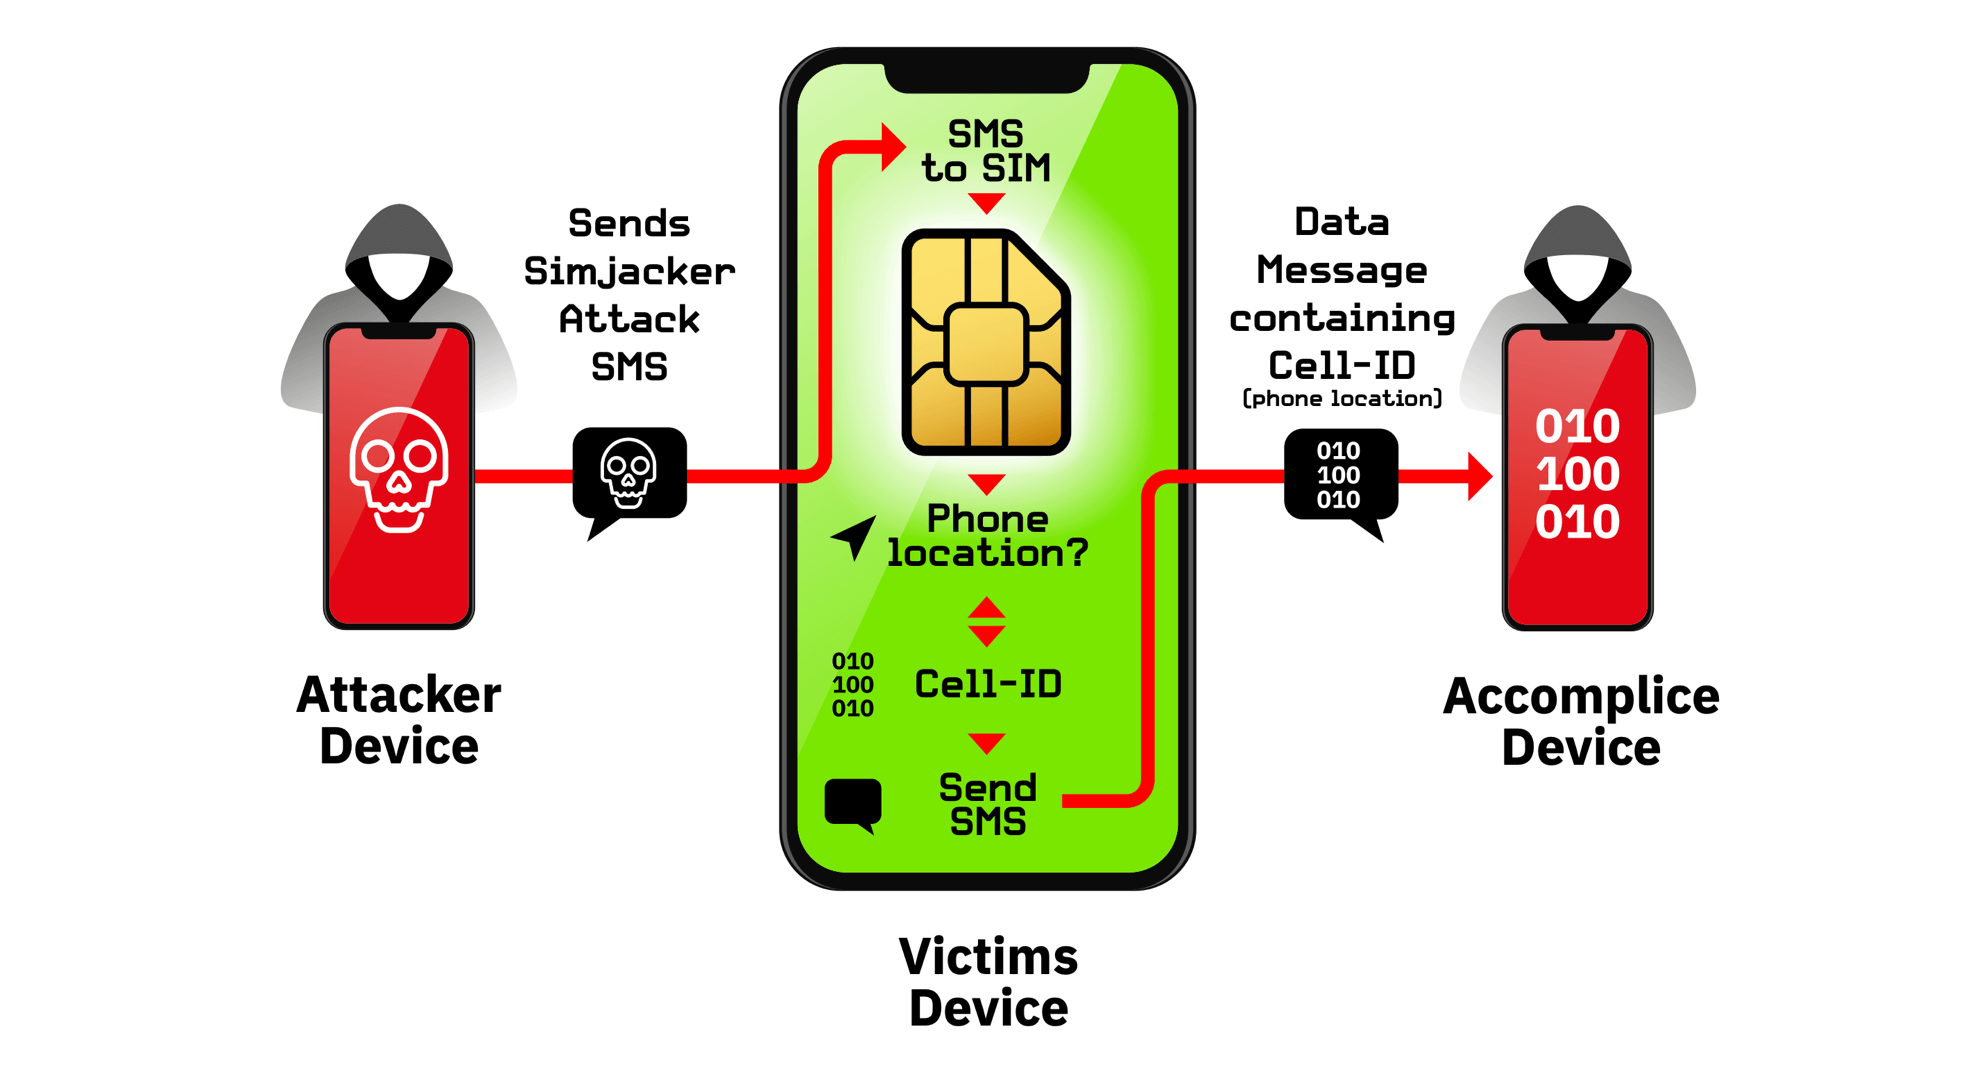
Infographic explaining the attack using Simjacker vulnerability | Photo by Simjacker.com
How does the Simjacker vulnerability work?
First, a hacker sends a malicious code to your phone through SMS. Then, the malicious code is read directly by your SIM card. The code then causes the S@T browser to send sensitive information to an accomplice device through SMS.
According to the report pulished by AdaptiveMobile Security regarding the vulnerability, the S@T browser is found on most SIM cards even though its development was abandoned many years ago. S@T browser was never updated, so it carries the risk of sending sensitive information to hackers when exploited successfully.
Sensitive information retrieved and transmitted by the S@T browser include location and the IMEI of an exploited device. The IMEI is a shorthand for International Mobile Equipment Identity, which is a 15 digit number unique to your smartphone that has some information about your device including its brand and model. As such, hackers can determine your exact location if you have a compromised SIM card, regardless of what device you have.
And the worst part of the attack is that you have no way of knowing that it has already been done since it all happens within the SIM card.
Origin and scope of the attack
The purpose for carrying an attack varies. However, the report traces the origin to an unspecified private company that works with governments to monitor individuals. So, there is a real possibility that it has been used to spy on us. And rightly so, since specific individuals were targeted in a certain country.
The report also warned that over one billion smartphones across all continents could be at risk to the vulnerability — and you could be one of them.
Response to the attack
In response to the discovered vulnerability, industry association SIMalliance has already put up recommendations for network providers to secure their networks. At this point in time, you can’t do anything to secure yourself from the vulnerability, unless you decided to go SIM-free.
But as a general rule of thumb, you shouldn’t just give your smartphone number like a free lunch. It also pays to update your smartphone once in a while, since some updates are designed to secure your phone from these kind of vulnerabilities and attacks.




Apps
Firefox ad reunites all your favorite memes from decades ago
The Numa Numa Guy, Annoying Orange, and Chocolate Rain are back!


Before Tung Tung Tung Sahur and Skibidi Toilet, the early internet was populated by charismatic personalities looking to make their presences felt in a land that didn’t have a lot of rules yet. As early users, we danced to “Dragostea din tei,” belted out “Chocolate Rain,” and copied “Shoes” word-for-word. Today, Firefox is bringing all those good memories back for a grand reunion.
In a new ad, the web browser featured ten of the biggest stars of the early internet including the aforementioned Numa Numa Guy, Tay Zonday, and Shoes’ Kelly. You can also see Annoying Orange, Chuck Testa, Overly Attached Girlfriend, Bad Luck Brian, Where the Hell is Matt?, the Apparently Kid, and the Success Kid.
Now, this isn’t just a reunion. The ad has a clear message about today’s most concerning issue: AI. Everything has “built-in AI, always asking, asking, asking,” as the Annoying Orange said.
“They make money by following us, and somehow, I’m the creepy one?” the Overly Attached Girlfriend asked.
All these famous personalities are asking what happened to the internet today. Obviously, the big takeaway is that we should all go back to Firefox.
Compared to other browsers, Firefox has a lot of built-in features that offer a lot of control for users. For one, it has its own VPN for privacy. Secondly, reflecting the ad’s message against AI, the browser has a toggle to minimize AI features.
SEE ALSO: Google illegally destroys 250,000 trees for a single AI data center
Apps
Salesforce introduces Slack Frontline for deskless workers
Simple, secure, mobile-first way for deskless teams across retail, healthcare, manufacturing, field service

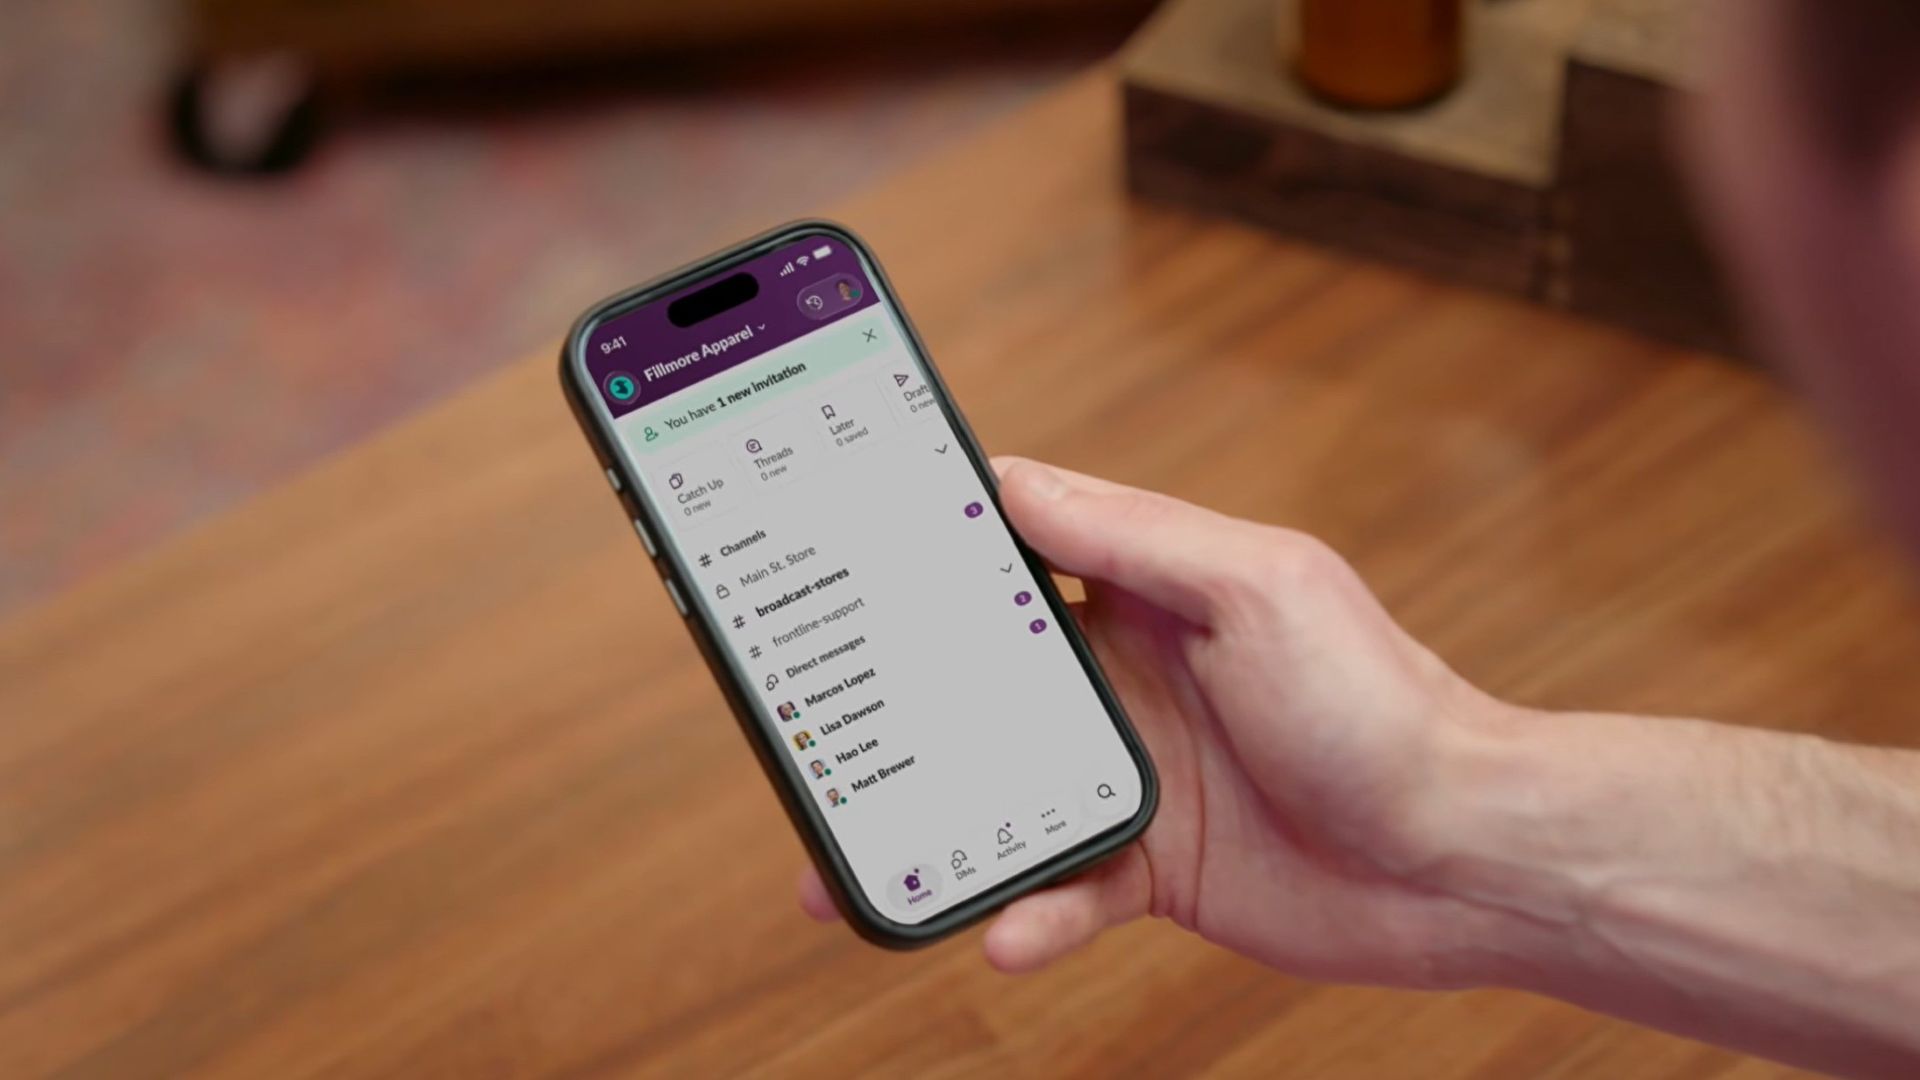
Salesforce is bridging the massive divide between corporate headquarters and deskless workers with the launch of Slack Frontline.
This new solution is designed specifically for retail associates, healthcare providers, factory workers, and field crews.
The mobile-first workspace brings communication, data, role-specific tools, and AI together in a single clutter-free app.
While frontline employees make up about 80 percent of the global workforce, they have historically been left out of workplace transformation, often relying on paper checklists, group texts, and broken communication loops.
Slack Frontline addresses these challenges by giving mobile workers up to 10 role-relevant channels, instant Huddles with headquarters, on-demand AI agents, and automated workflows.
Backed by Salesforce data and enterprise-grade security, the platform lets IT teams govern the entire workforce under one secure layer with employee ID sign-ins, multifactor authentication, and compliance configurations like HIPAA.
This ensures that critical updates, training materials, and shift handoffs reach workers directly in their pockets without needing corporate email addresses or shared terminals.
Moreover, the platform is tailored to transform operations across multiple industries, including retail, home healthcare, manufacturing, hospitality, and field services.
For instance, retail teams can instantly sync promotions and monitor inventory, while healthcare professionals can securely review patient histories and coordinate care on the go.
Manufacturing and hospitality teams benefit from drastically reduced downtime and faster issue resolution, cutting response times significantly.
Slack Frontline is available now as an add-on for businesses on the Slack Enterprise+ plan.
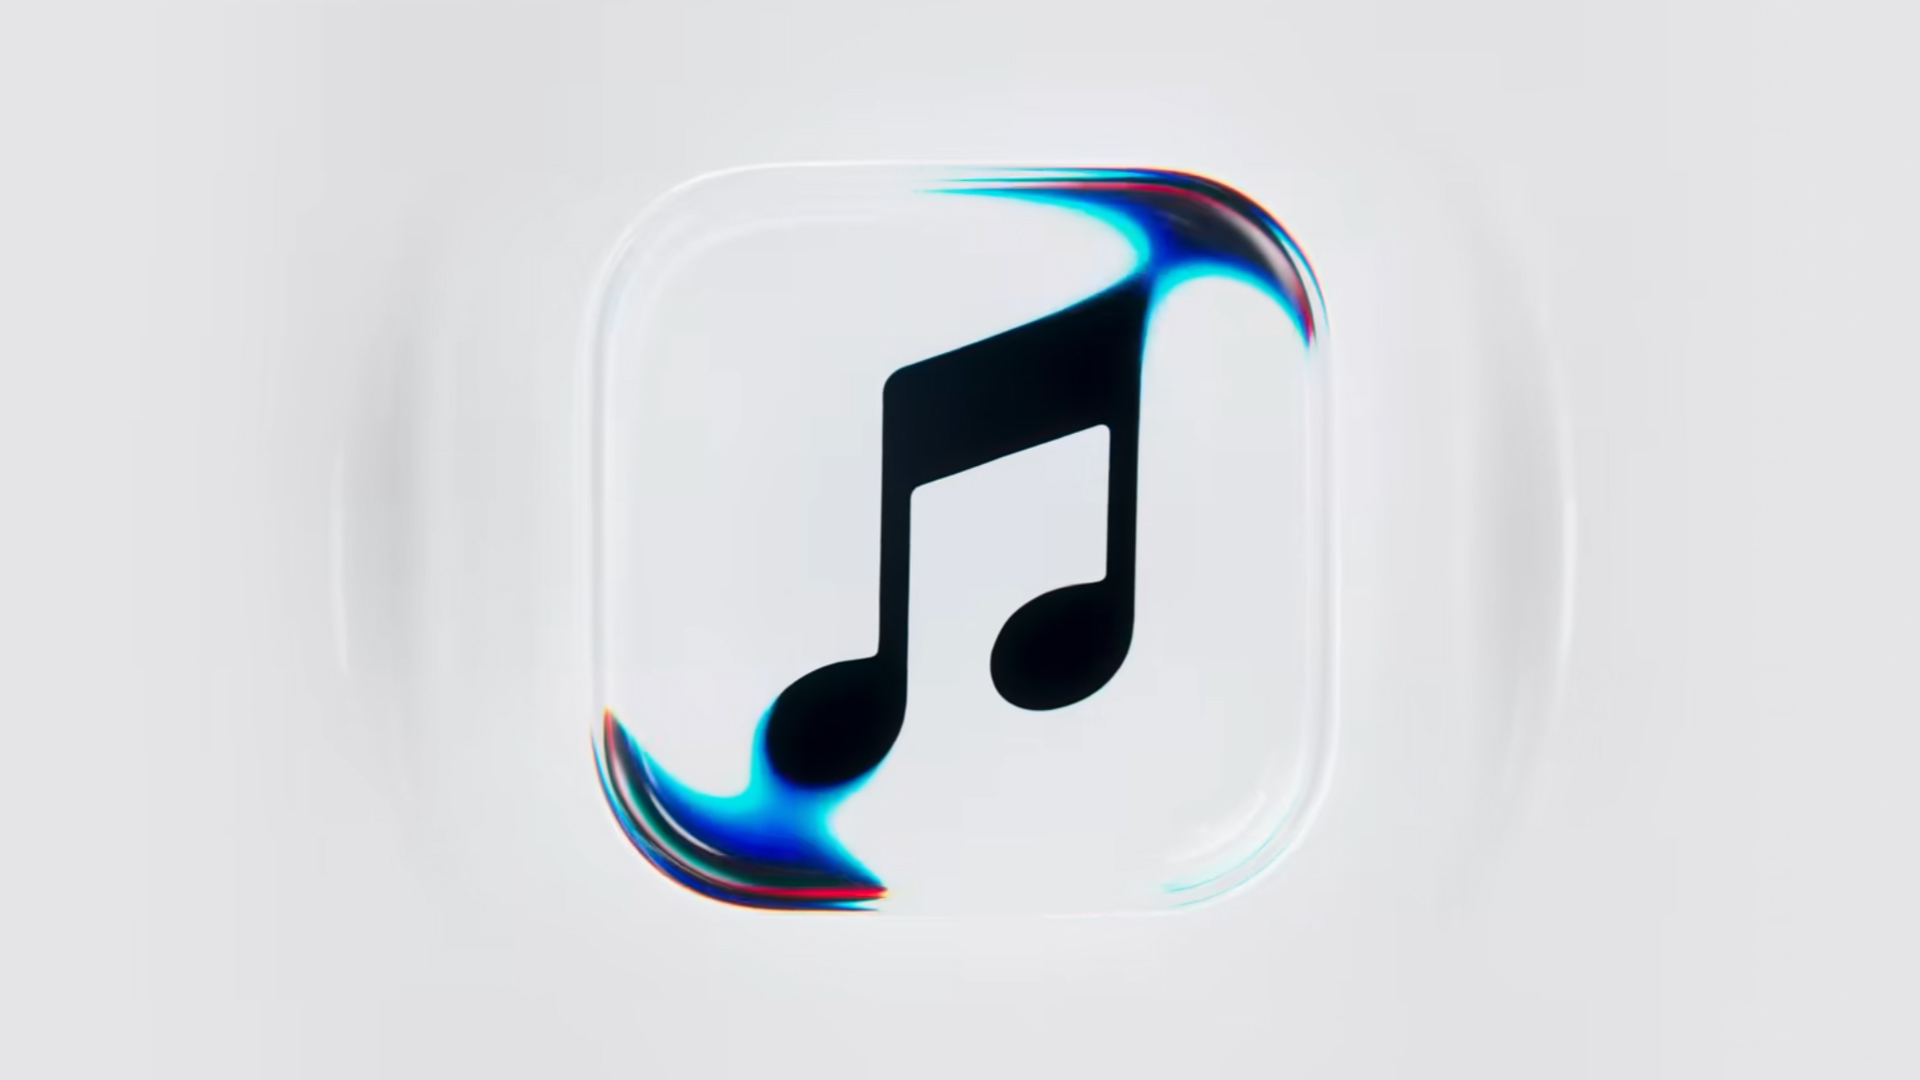
Apple Music is getting a revamp. In one of the tamer things going on with the brand today, Apple has introduced a new design language for its native music streaming platform.
In the midst of all the hubbub surrounding the iPhone Duo, Apple released a change in the visual identity of Apple Music. Rather than a static logo, the platform’s newest evolution offers a dynamic look that melds Liquid Glass and the power of sound together.
Confirmed through a behind-the-scenes video, Apple says that the new aesthetic was made with practical effects. Music producer Fred Again and NEST Acoustics submerged the platform’s logo in a tank of mineral oil and creating ripples with sound. The new language matches well with the chrome aesthetic typical of today’s trends and… well, Liquid Glass, of course.
Apple says that the more ripple-filled version will play before longer content like concert recordings (similar to Netflix’s startup stinger). Meanwhile, a black-and-white version will replace the app’s icon currently colored red and white. Current previews show off a simple logo, but it’s unknown whether Apple is adding a but more elements when the final version drops.
The updated version will debut for users after next week’s iOS 27.2 and macOS 27.2 updates.
SEE ALSO: Apple iPhone Duo Unboxing and Hands-on


ROG G700 review: The best prebuilt PC you can get off the shelf
This PC will make you stop worrying about specs.


HP OMEN Max 16 review: Gamer-maxxing in deep black
Peripherals deemed necessary to max this out


vivo V80 review: Good phone, tough sell
A capable travel companion

Smart boosts 5G network in Siargao for World Surf League event

The next Elder Scrolls game is called Sentinel

4 new nutribullet kitchen essentials to make holiday hosting easier

Inside Infinix’s first global concept store in Bali

Wild Rift Patch 7.3, celebrates K/DA comeback

OPPO Find X10 Series launches globally October 21

vivo V80 debuts with ZEISS cameras

Garmin Enduro 4 promises up to 320 hours of battery life

Your coffee nook is getting a makeover with Starbucks’ holiday collections

Dragon’s Dogma 2: Dark Arisen launches with new Official Pawns


-
 Lifestyle3 days ago
Your coffee nook is getting a makeover with Starbucks’ holiday collections
-
Gaming2 weeks ago
HP OMEN Max 16 review: Gamer-maxxing in deep black
-
 Lifestyle5 days ago
Sticker season is back, and so is the planner your ~friends~ might fill in for you
-

 Apps2 weeks ago
Apple Music is getting a Liquid Glass makeover
-
 Gaming2 weeks ago
FINAL FANTASY RESONANCE now available across major platforms
-
Gaming1 week ago
ROG G700 review: The best prebuilt PC you can get off the shelf
-
 Gaming3 days ago
Wild Rift Patch 7.3, celebrates K/DA comeback
-
 Gaming1 week ago
PlayStation unveils Prism Collection